All articles
Latest first
Stop Handing Your AI Agents (and Your Deploy Scripts) the Keys to Everything
Personal access tokens give deploy scripts and AI agents unlimited blast radius. The fix is short-lived GitHub App tokens minted per deploy and revoked seconds later.
Read article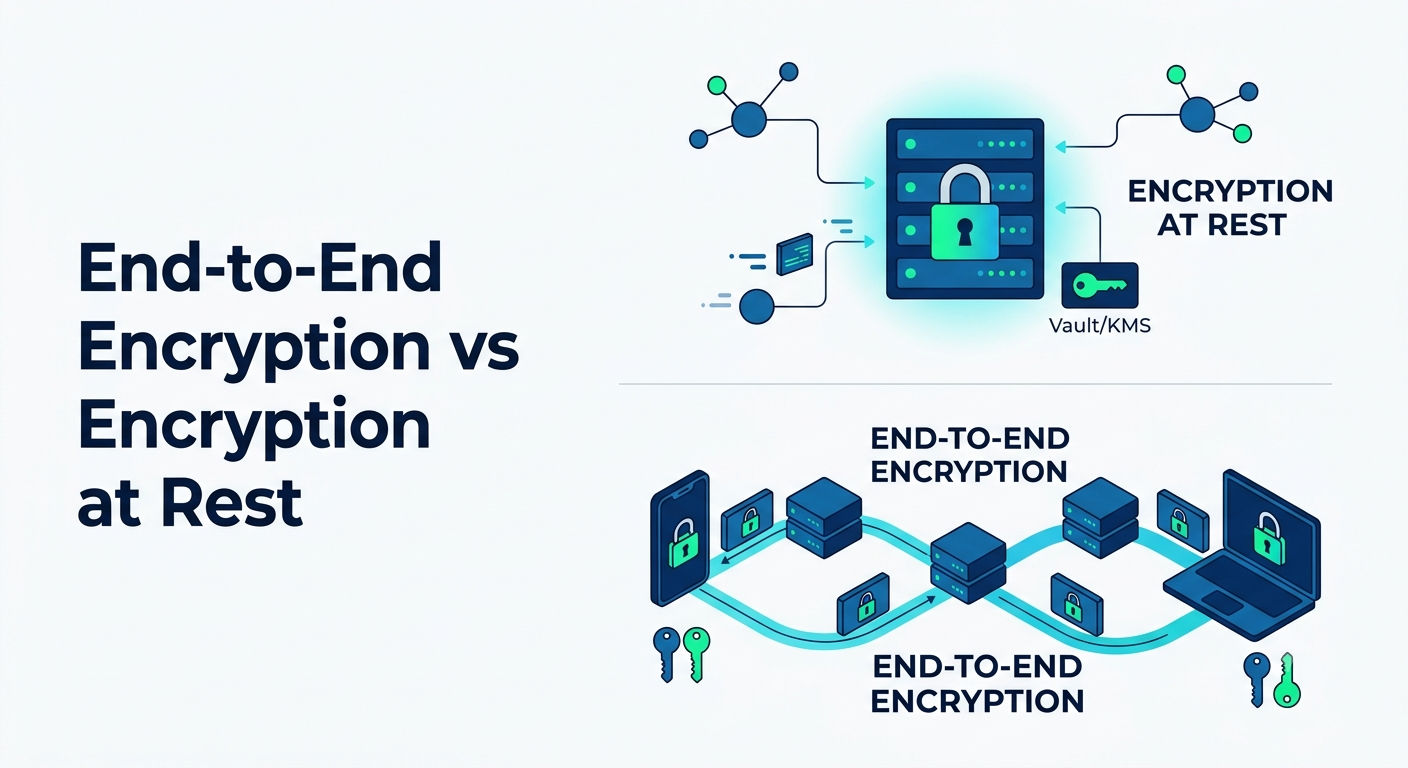
End-to-End Encryption vs Encryption at Rest
Encryption at rest and end-to-end encryption are not the same promise. A practical design for real E2E data storage, and the tradeoffs most teams skip.
Read article
Break the Glass, Not the Trust: A Developer's Case for Structured Data Access
How the "break-glass" exception process resolves the oldest tension in software delivery — the need for real data versus the need to protect it — and why it deserves a place in every DPDPA compliance...
Read article
Dead Letter Queue (DQL) Debug, Reprocess, Never Lose a Job
Retries run out eventually. A Dead Letter Queue catches what's left — but it's not a magic bullet. Redrive policies, poison jobs, FIFO caveats, and why observability matters.
Read article
How I Stopped Getting Surprised by My Own Code
Explore first, document the plan, then build. This one shift stopped my code reviews from being full of surprises — and made every feature genuinely easier to trust.
Read article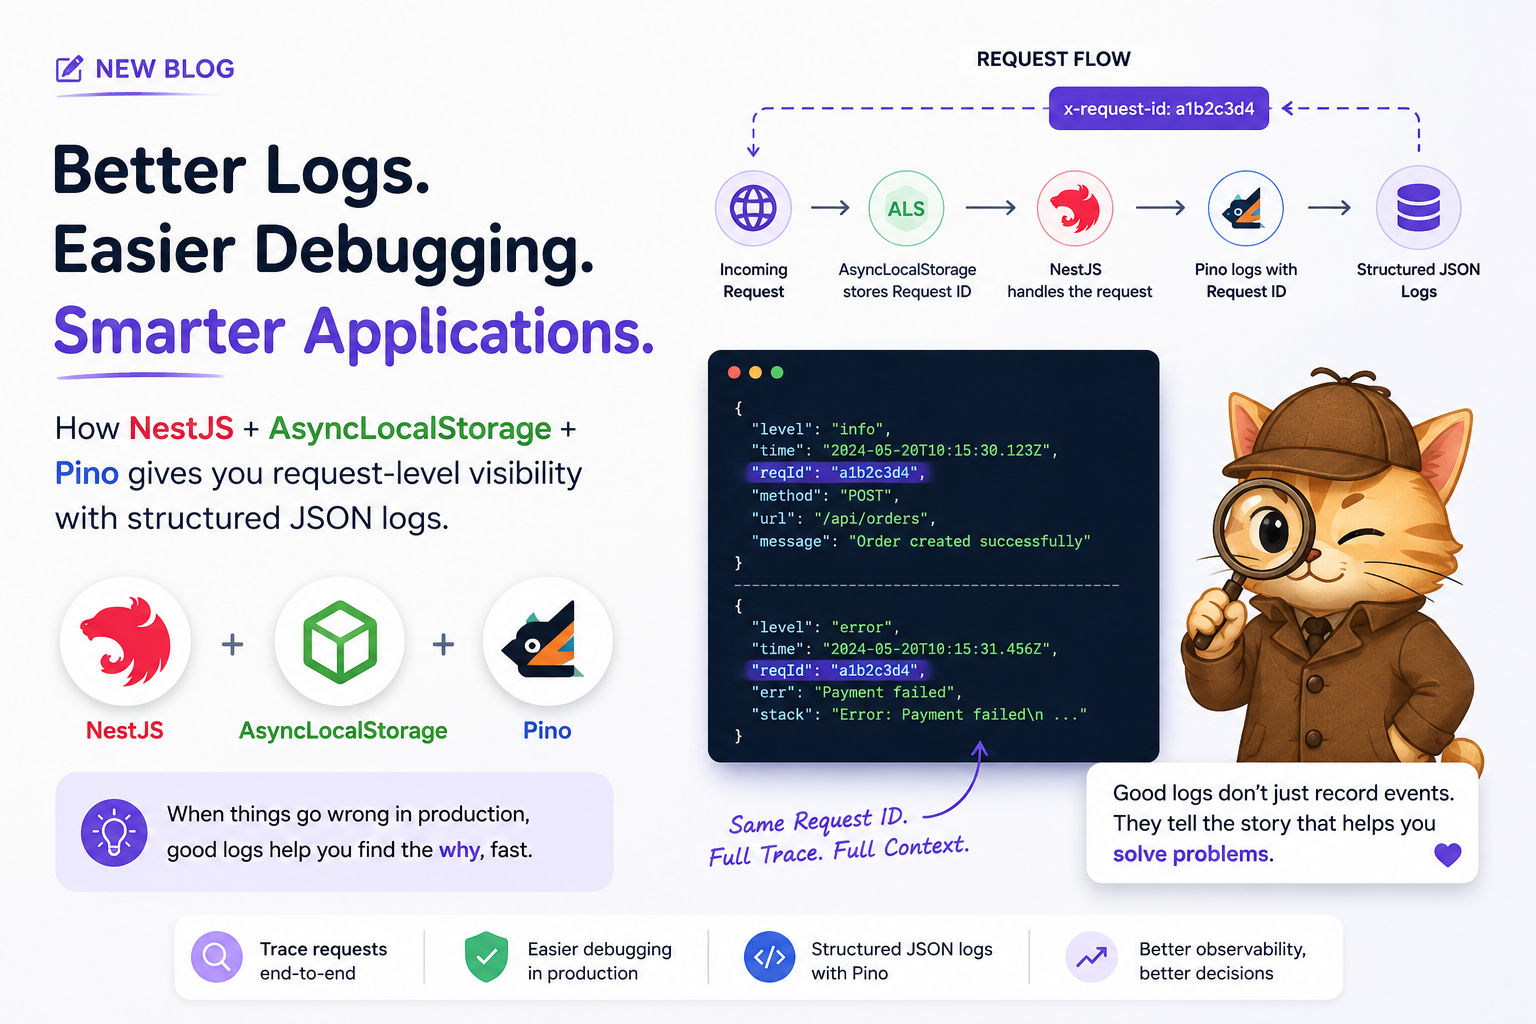
Logging Is Infrastructure: What I Learned Wiring Pino Into a NestJS API
Logging felt like a boring swap — console.log for pino. Instead it unlocked structured, traceable, secure production logs. Here's why AsyncLocalStorage, JSON, and request IDs change everything.
Read article
Event-Driven Queue Architecture in NestJS: A System Design Perspective
Scalable NestJS backends live or die on how queue infrastructure is separated from domain logic. Here's the system design reasoning behind an event-driven BullMQ architecture that actually holds up.
Read article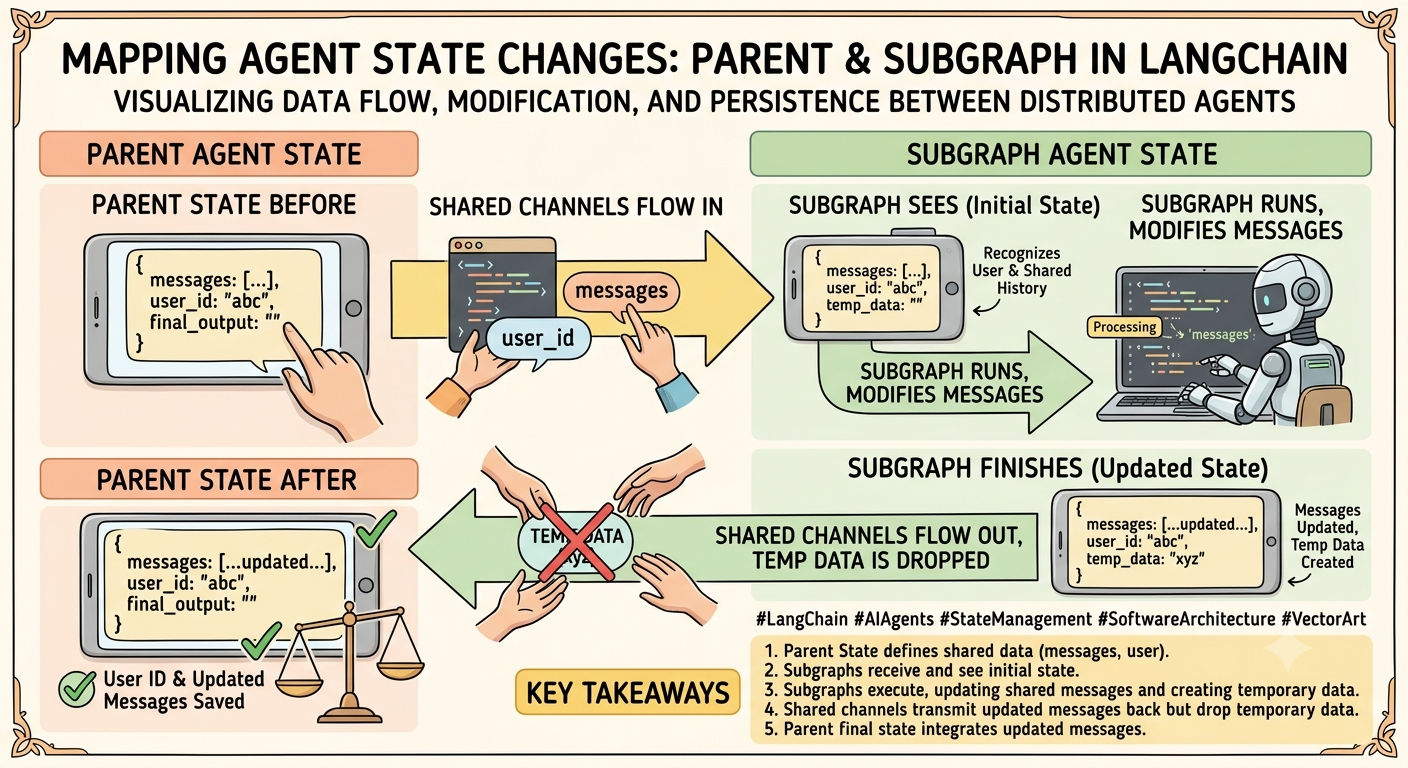
LangGraph Subgraphs: What "Shared Channel Names" Actually Means
I was wiring up a LangGraph parent-subgraph today and couldn't figure out how data flows. Turns out it's simpler than the docs make it sound — matching key names is all it takes.
Read article
Field-Level Encryption With Searchable Blind Indexes: A Practical SOC2 Control Worth Understanding
Most security controls protect the perimeter. Field-level encryption protects the data itself. Using CipherSweet's blind index approach, you can encrypt sensitive columns at the application layer and...
Read article